axio - kn

test

Posts by Axio:

AgendaWeek: Key Questions for Boards to Vet Ransomware Playbooks

AgendaWeek: Key Questions for Boards to Vet Ransomware Playbooks

With the ever-increasing number of ransomware attacks, boards are quickly re-evaluating the assorted cybersecurity policies they have in place. AgendaWeek [subscription required to read article] examines the response plans and playbooks CISO’s and management teams have in the event of a ransomware attack. The Colonial Pipeline event has instilled a sense of urgency into board members, and has encouraged them to review both their perceived threat level of ransomware as well as their preventative measures.
AP News: Major U.S. pipeline halts operations after ransomware attack

AP News: Major U.S. pipeline halts operations after ransomware attack

One of the largest ransomware attacks in U.S. history occurred last Saturday when Colonial Pipeline was successfully targeted by an unnamed group. As per this AP News article, Colonial Pipeline, responsible for 45% of fuel consumed on the east coast, has halted all pipeline operations indefinitely to deal with the attack. While unlikely, this shutdown can lead to changes in gasoline supply and prices if the issue prolongs. The issue, however, is large enough that President Biden was briefed on the issue Saturday morning, and the federal government is working with Colonial Pipeline to assess the attack, repair operations, and avoid disruptions.

Announcing New Features To Our Free Ransomware Preparedness Assessment Tool

Announcing New Features To Our Free Ransomware Preparedness Assessment Tool

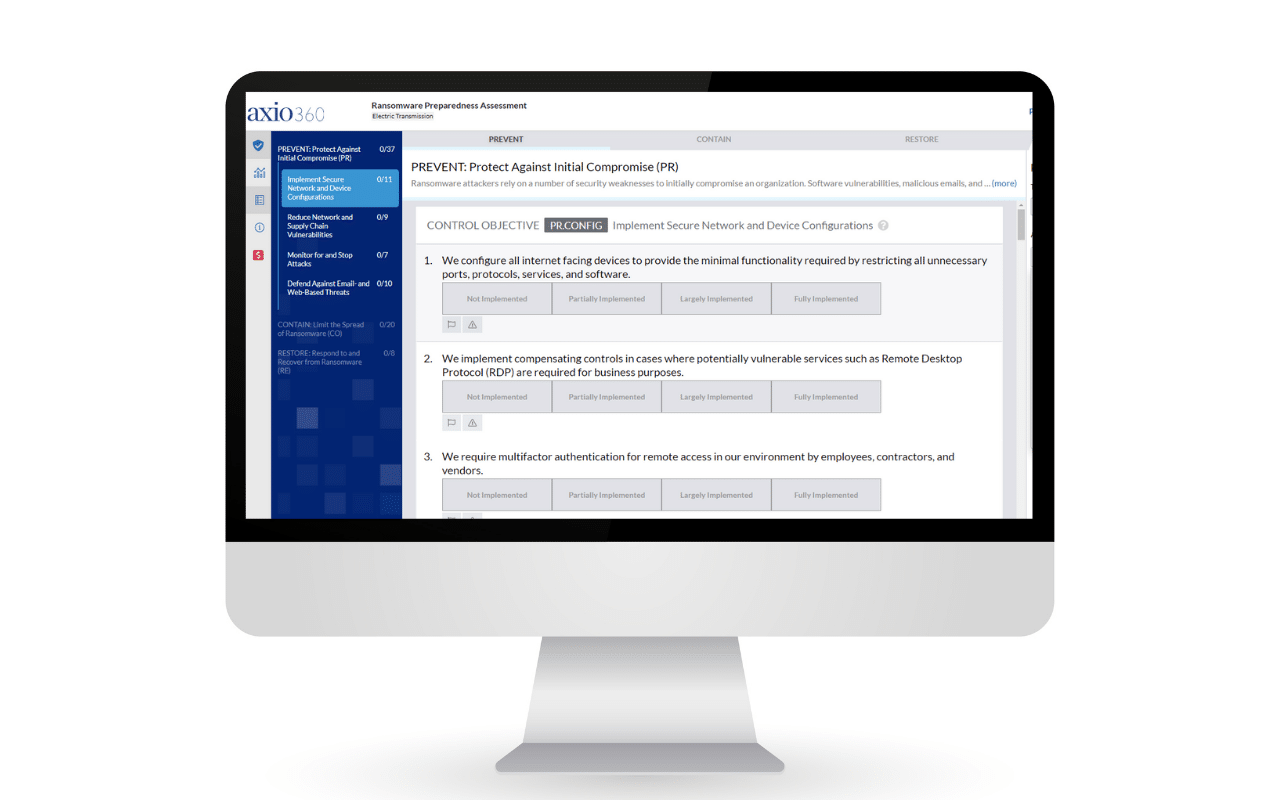
In light of recent cyber attacks at Colonial Pipeline and other critical infrastructur­e operators, we are releasing an updated version of our Ransomware Preparedness Assessment Tool with new features designed to help leaders illuminate the gaps in their cybersecurity posture that directly cause increased susceptibility to ransomware attacks. Users can leverage these insights within Axio360 to accurately quantify the financial damage that could occur to drive more comprehensive cyber risk management.

A Timeline of Frameworks for Cybersecurity and Compliance

A Timeline of Frameworks for Cybersecurity and Compliance

In the world of cybersecurity, IT and risk managers have long touted the benefits of using maturity models and control frameworks to help assess preparedness. Specifically, these models and frameworks have helped create more ways for companies and governments to evaluate resiliency.

A Historical Perspective of Cybersecurity Frameworks

A Historical Perspective of Cybersecurity Frameworks

In 2021, cybersecurity risk has become a prominent  concern for  businesses and governments around the world. The past year has shown that no amount of defensive technology can protect against malicious intent from a variety of adversaries including a new breed of attacker that leverages the financial resources of nation-states and the ingenuity of the world’s most advanced cyber criminals. These  attacks can cause millions of dollars’ worth of damage to companies by compromising valuable data and infrastructure, interrupting business operations, and damaging organizational reputation, sometimes irreparably.

The Hole in Biden’s Infrastructure Plan That Leaves Us All Vulnerable

The Hole in Biden’s Infrastructure Plan That Leaves Us All Vulnerable

Last week President Biden, laid out a $2 trillion proposal to rebuild America. Of this $2 trillion, $100 billion will go to modernizing the power grid, $100 billion to expand broadband access, $100 billion to build new schools, $620 billion for transportation infrastructure, as well as many green initiatives including 500K charging stations and more. But the question is, how well is the plan truly prioritizing cyber risk?

Top 5 Cyber Risk Questions Board Members Ask Axio

Top 5 Cyber Risk Questions Board Members Ask Axio

Executive Summary

Board Members Request Business-Centric Cyber Risk Reporting

Recently, our board member customers have expressed great interest in understanding cyber risk in business terms. Proactive governance is becoming essential considering the increasing physical and cyber devastation over the past few years. Board reporting is shifting from reliance on a ‘defend and protect’ mindset to a more capable ‘mitigate and manage’ methodology.

A Risk Management Wake-Up Call

A Risk Management Wake-Up Call

Our world is digitally dependent. The recent Oldsmar water attack on internet-connected control systems served as a clarion reminder: hackers almost succeeded in poisoning the water supply in Florida without setting foot inside the physical premises. As our reliance on digital systems grow, cyber risk becomes ever pervasive, enterprise organizations need to reset their approaches to managing cyber risk. Many organizations have a siloed approach to addressing their risks and ultimately, this impedes their ability to function optimally as a business. Axio’s VP of Cyber Risk Engineering, Lisa Young, led a webinar investigating this issue hosted by Society of Information Risk Analysts.