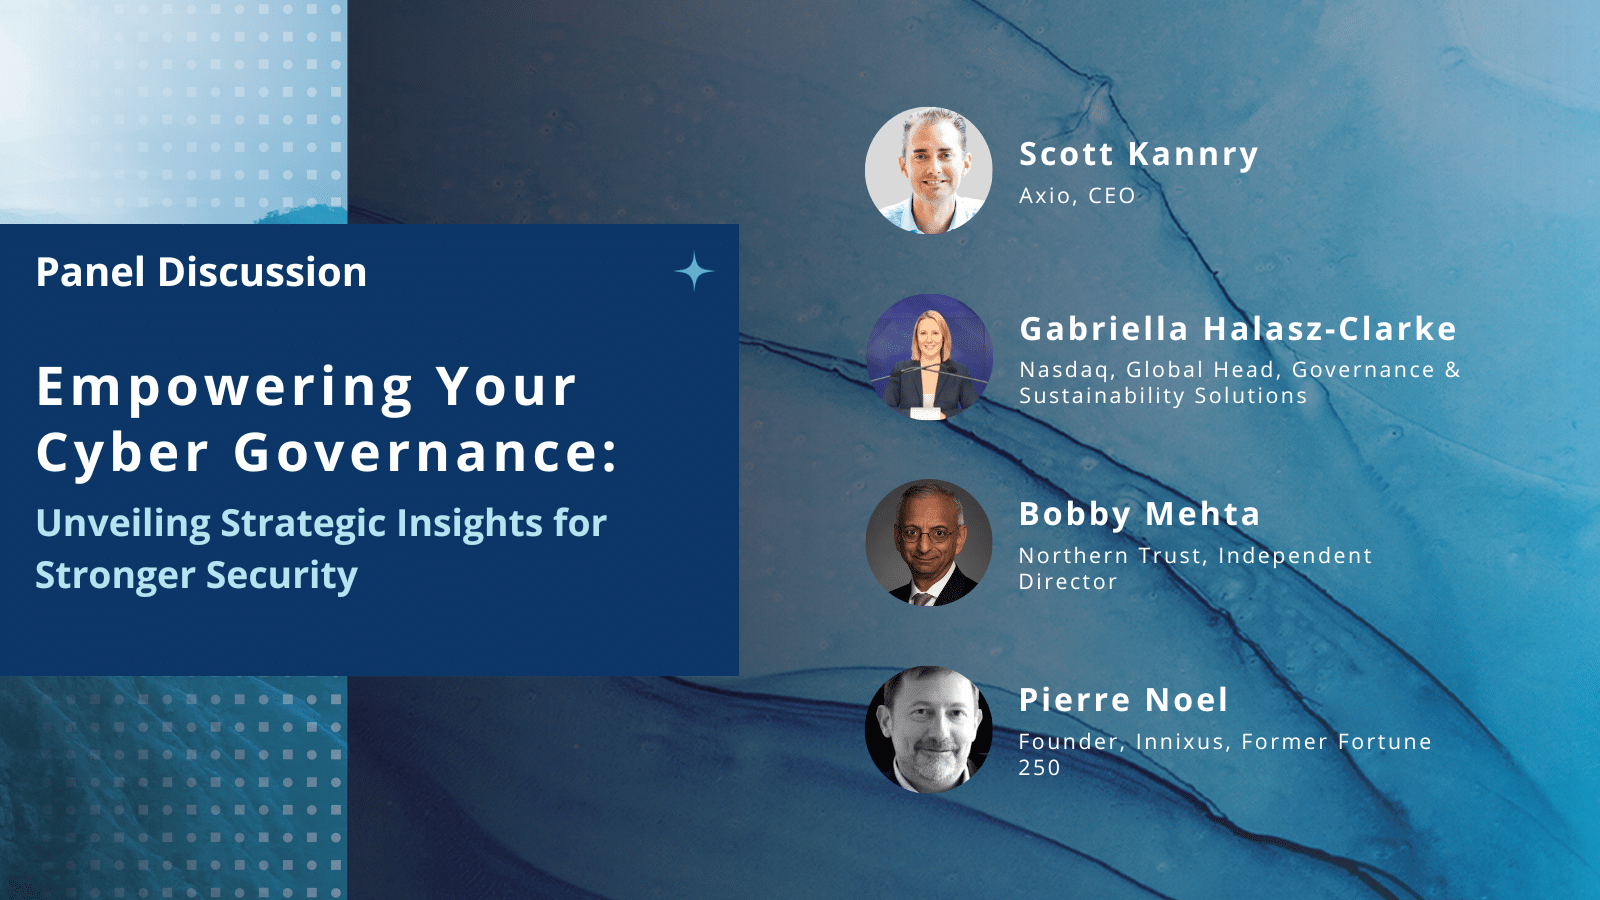
Webinar Recap – Axio & the Nasdaq Center of Board Excellence Team Up to Host a Panel Discussion Around Empowering Your Cyber Governance: Unveiling Strategic Insights for Stronger Cybersecurity
NEW YORK – July 14, 2025 – The Nasdaq Center for Board Excellence (NCBE) today announced a strategic partnership with Axio, a leading provider of cyber risk quantification and management solutions, intended to enhance cybersecurity oversight capabilities for corporate boards.
In a timely and candid webinar hosted by Axio, leading experts discussed what’s working (and what’s not) in industrial cybersecurity as we look toward 2025. Featuring insights from cybersecurity veteran Matt Morris, OT product expert Grayson Estes, and Axio President David White, the session revealed a common theme: many organizations are still missing the mark on the fundamentals, even as threats grow more advanced.
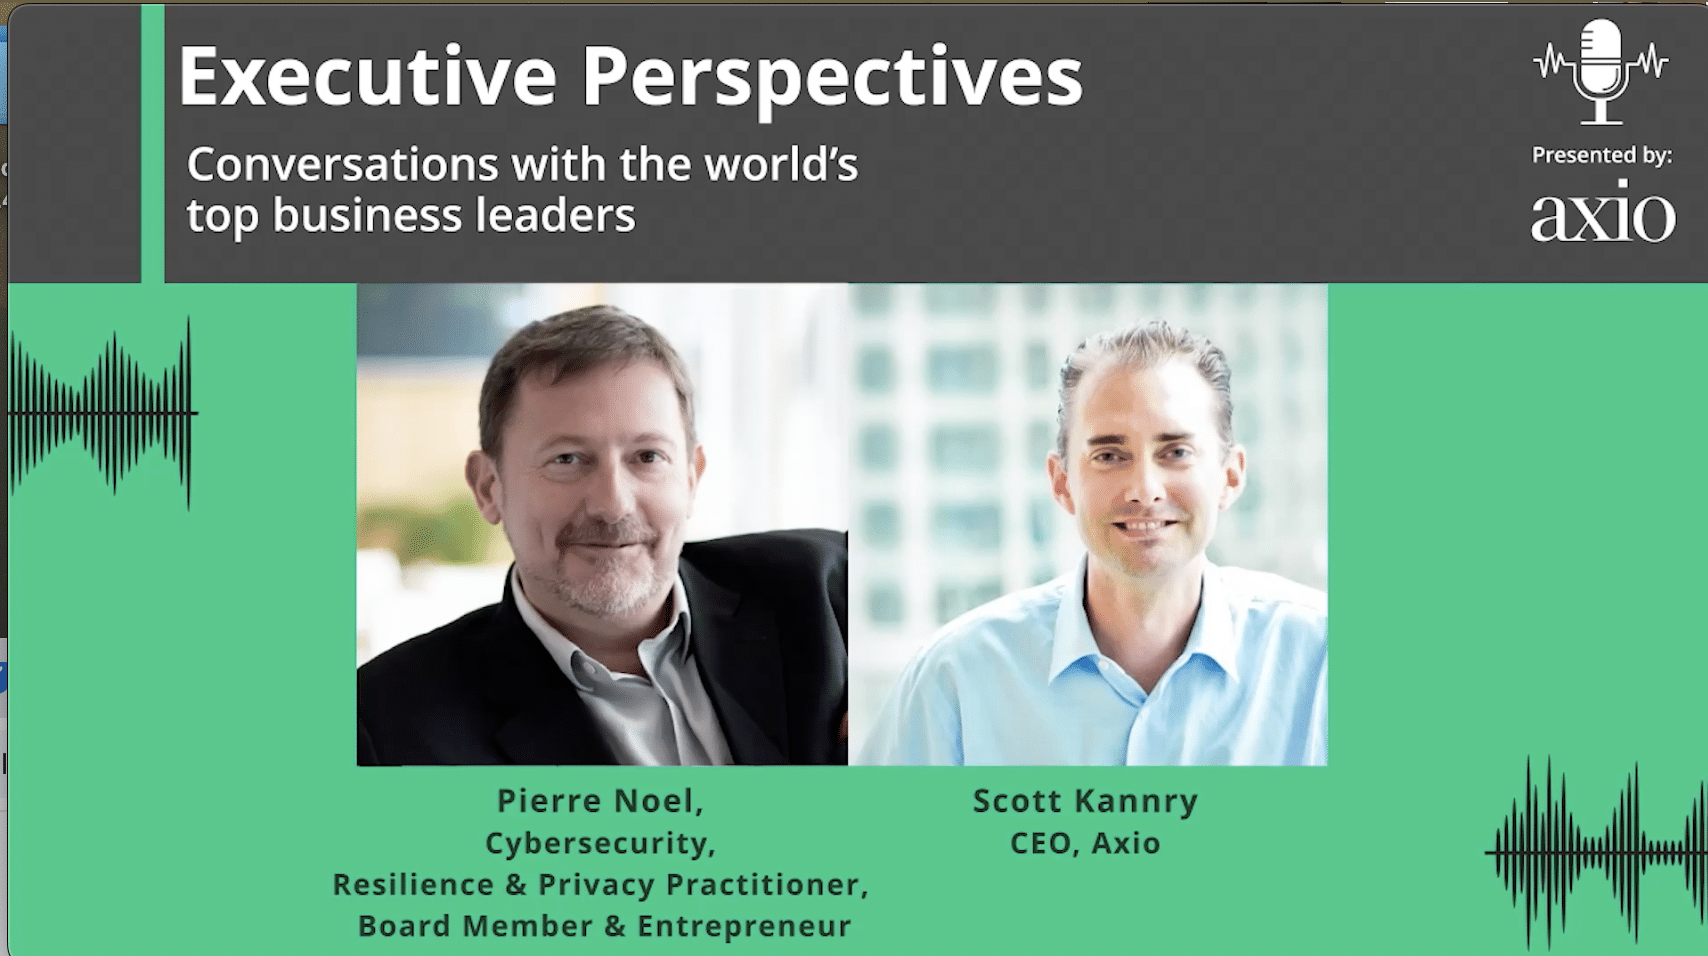
In this edition of Axio’s Executive Insight Series, Scott Kannry, CEO of Axio, sits down with Pierre Noel, former CISO of Microsoft Asia and Huawei, to discuss the evolution of cybersecurity leadership, managing cyber risk, and the importance of resilience in an ever-changing digital landscape. With decades of global experience advising enterprises and governments, Pierre shares practical insights for today’s security leaders, from communicating risk effectively to building diverse and resilient cybersecurity teams.
In the latest episode of Axio’s Executive Insight Series, CEO Scott Kannry sits down with Ryan Surry, Founder and Managing Director of Intaso, to discuss the evolving role of security leadership, the challenges facing CISOs today, and the state of the cybersecurity job market. Ryan brings a unique perspective, having placed top-tier cybersecurity professionals for years, and his insights shed light on the shifting priorities and expectations of security leaders and organizations alike.

The financial services sector is facing a major shift as the FFIEC Cybersecurity Assessment Tool (CAT) sunsets on August 31. Thousands of financial institutions worldwide have relied on the CAT to assess cybersecurity risk and maturity. Now, with its retirement, organizations must identify a new framework to guide their cybersecurity programs.
In a world in which cyberattacks have become both more frequent and costly, organizations are under growing pressure to manage digital threats more effectively. Cyber Risk Quantification (CRQ), a means of systematically evaluating cyber risks, has been a cornerstone of these efforts. But just as the threat landscape has evolved over time, so must the tools used to address it.
In a thoroughly digital world, cyber incidents can have a huge financial impact, with the average cost of a data breach skyrocketing to $4.88 million. Still, too many businesses struggle to align cybersecurity strategies with broader organizational goals, leaving them ill-equipped to navigate the evolving threat landscape.

In the latest episode of Axio’s Executive Insight Series, CEO Scott Kannry sat down with Jena Valdetero, Co-Chair of Greenberg Traurig’s U.S. Data, Privacy and Cybersecurity Group. Their conversation delved into critical aspects of cybersecurity governance, incident preparedness, and regulatory compliance, offering practical advice for organizations navigating today’s complex cyber risk landscape.

In a recent webinar, David White, President at Axio, joined Shawn Bilak, Senior Cybersecurity Advisor at Southern Company, and Eric Cardwell, Senior Advisor at Axio, to discuss the evolution of cybersecurity assessments. Together, they explored how organizations can streamline processes, enhance decision-making, and drive meaningful improvements using modern tools and approaches.