
When it comes to M365, one of the most common questions we hear from leaders is : “We’re paying for Microsoft 365 – but what are we actually getting back?”
It’s the...
When it comes to M365, one of the most common questions we hear from leaders is : “We’re paying for Microsoft 365 – but what are we actually getting back?”
It’s the...

We’re pleased to confirm that we have successfully passed our ISO 27001 recertification audit following the five-day assessment in December.
For UK businesses, protecting data is a legal, commercial and reputational requirement. As a Managed Service Provider, trust is vital: our customers need to rely on us following best practice so we can ensure we’re protecting them and their customers, too.
Matt Westney, our COO, said: “ISO 27001 is one of the clearest ways to prove that trust is earned and maintained. This recertification reinforces our trusted security posture, supports compliance, and ensures we continue to protect customer and company data in line with internationally-recognised standards. As with ISO 9001, it also helps us drive ongoing continuous improvement; this is a great result, demonstrating our commitment to maintaining high standards of ISMS and reflects the strong information security practices embedded across the business, as well as our whole team’s cooperation during the audit.”
In this blog, we explain what ISO 27001 is, why it matters to an MSP, and how it benefits both providers and their clients.
ISO 27001 is the international standard for information security management. It sets out how an organisation should manage and protect sensitive information, which covers customer data, financial records and intellectual property.
The standard essentially focuses on risk. It requires a business to understand what data it holds, where it lives, who can access it and how it is protected. Certification is then awarded by an independent body after a formal audit and must be maintained through regular reviews.
MSPs have privileged access to client systems and data which, unsurprisingly can make them a high value target for cyber attacks.
ISO 27001 helps MSPs reduce this risk by putting structured controls in place. It moves security away from ad hoc tools and towards a consistent, documented approach. This includes clear policies, defined responsibilities and tested processes.
For an MSP, certification shows that security is built into daily operations, not bolted on when something goes wrong. However, for its clients, there’s many other reasons why having ISO 27001 is important too.
Clients want reassurance that their data is safe. Many now ask about security standards as part of procurement and, especially for certain industries, some will not work with suppliers who lack recognised certification.
ISO 27001 provides clear, independent proof that an MSP takes information security seriously. It is widely recognised and understood across industries. This makes conversations with clients simpler and more credible.
Rather than relying on promises, an MSP can point to a formal standard that is audited and maintained. This builds confidence and shortens sales cycles.
UK organisations face growing regulatory pressure around data protection. The UK GDPR policies place strict obligations on how personal data is handled. Clients often rely on their MSP to help them meet these requirements.
While ISO 27001 is not a legal requirement, it aligns closely with data protection principles. It supports better access control, incident management and data handling practices.
For MSPs, this reduces the risk of compliance failures and the reputational damage that follows. It also helps clients demonstrate due diligence when working with third parties.
ISO 27001 isn’t just about security technology or even a ‘tickbox exercise’ – it also improves how an MSP operates.
The standard encourages clear documentation and consistent processes. Staff understand their responsibilities and know how to respond to incidents. Risks are identified and reviewed regularly, rather than ignored.
Over time, this leads to fewer surprises and better decision making, so that security becomes part of everyday work, rather than a separate project.
For businesses selecting an MSP, ISO 27001 certification is a strong indicator of quality. It shows that security is governed at board level and embedded across the organisation.
Whether you’re looking to move MSPs or with your existing MSP, ask whether the certification covers the services you use and how often audits take place – a credible MSP will be open and transparent.
In a world where data breaches are common and confidence is fragile, ISO 27001 helps MSPs stand out for the right reasons. Want to work with experts you can trust? Contact us today.
Over the past 12 months, we’ve grown rapidly. It might be the penultimate week of the year, but we’re excited to welcome Olivia Langdon and Luke Raisborough to the...

Last month, Microsoft shared that they saw the future of work being shaped by “Frontier Firms”, which they defined as organisations that are human-led and...

How confident are you that your organisation truly understands the threats moving across its IT environment right now?
In an increasingly dangerous cyber security landscape, too many businesses continue to operate with blind spots; unseen vulnerabilities, unmonitored systems and outdated assumptions create risks that grow quietly in the background until they become business critical.
This is why our latest product innovation is so important is so important. Arc Threat Lens is a cyber security assessment tool giving you a comprehensive, holistic view of your full IT estate maturity; it brings clarity to complexity and gives leaders a complete, holistic view of their environment along with a quarterly report for board level to understand progress and your ongoing position.
Turning technical risk into clear, straightforward insight that executives can act on with confidence, Threat Lens provides the reporting and visibility organisations need to make informed security decisions before issues become incidents.
We sat down with Mark Darrah, our CTO, to learn more.
So what is Threat Lens? Mark explains: “If you imagine a traditional pen test environment, what we do is look at a single source. We’ll do a penetration test against that environment at single point in time, and from there we’ll actually derive what needs to be remediated. Obviously this is still important, but with all the well-publicised hacks across 2025, it’s pretty obvious that businesses need to be looking at their environment holistically, too. It’s not about just looking at a single point of entry, because there’s no point securing something over here if you’ve got an open gate over there – you’re just going to let threats through.
“Threat Lens looks at the entire environment holistically. We can look at all elements from Microsoft Azure, Microsoft 365 Internal Resources, AWS Intune, G-suite, SharePoint on-prem, GitHub, local nodes, servers, Active Directory entry… I could go on! Our approach brings all of these security vectors together, combining proactive, monthly scanning on a retainer basis, so that businesses can know what their security position is in a point in time, whilst also tracking progress and knowing what their costs are on an ongoing basis, too.”
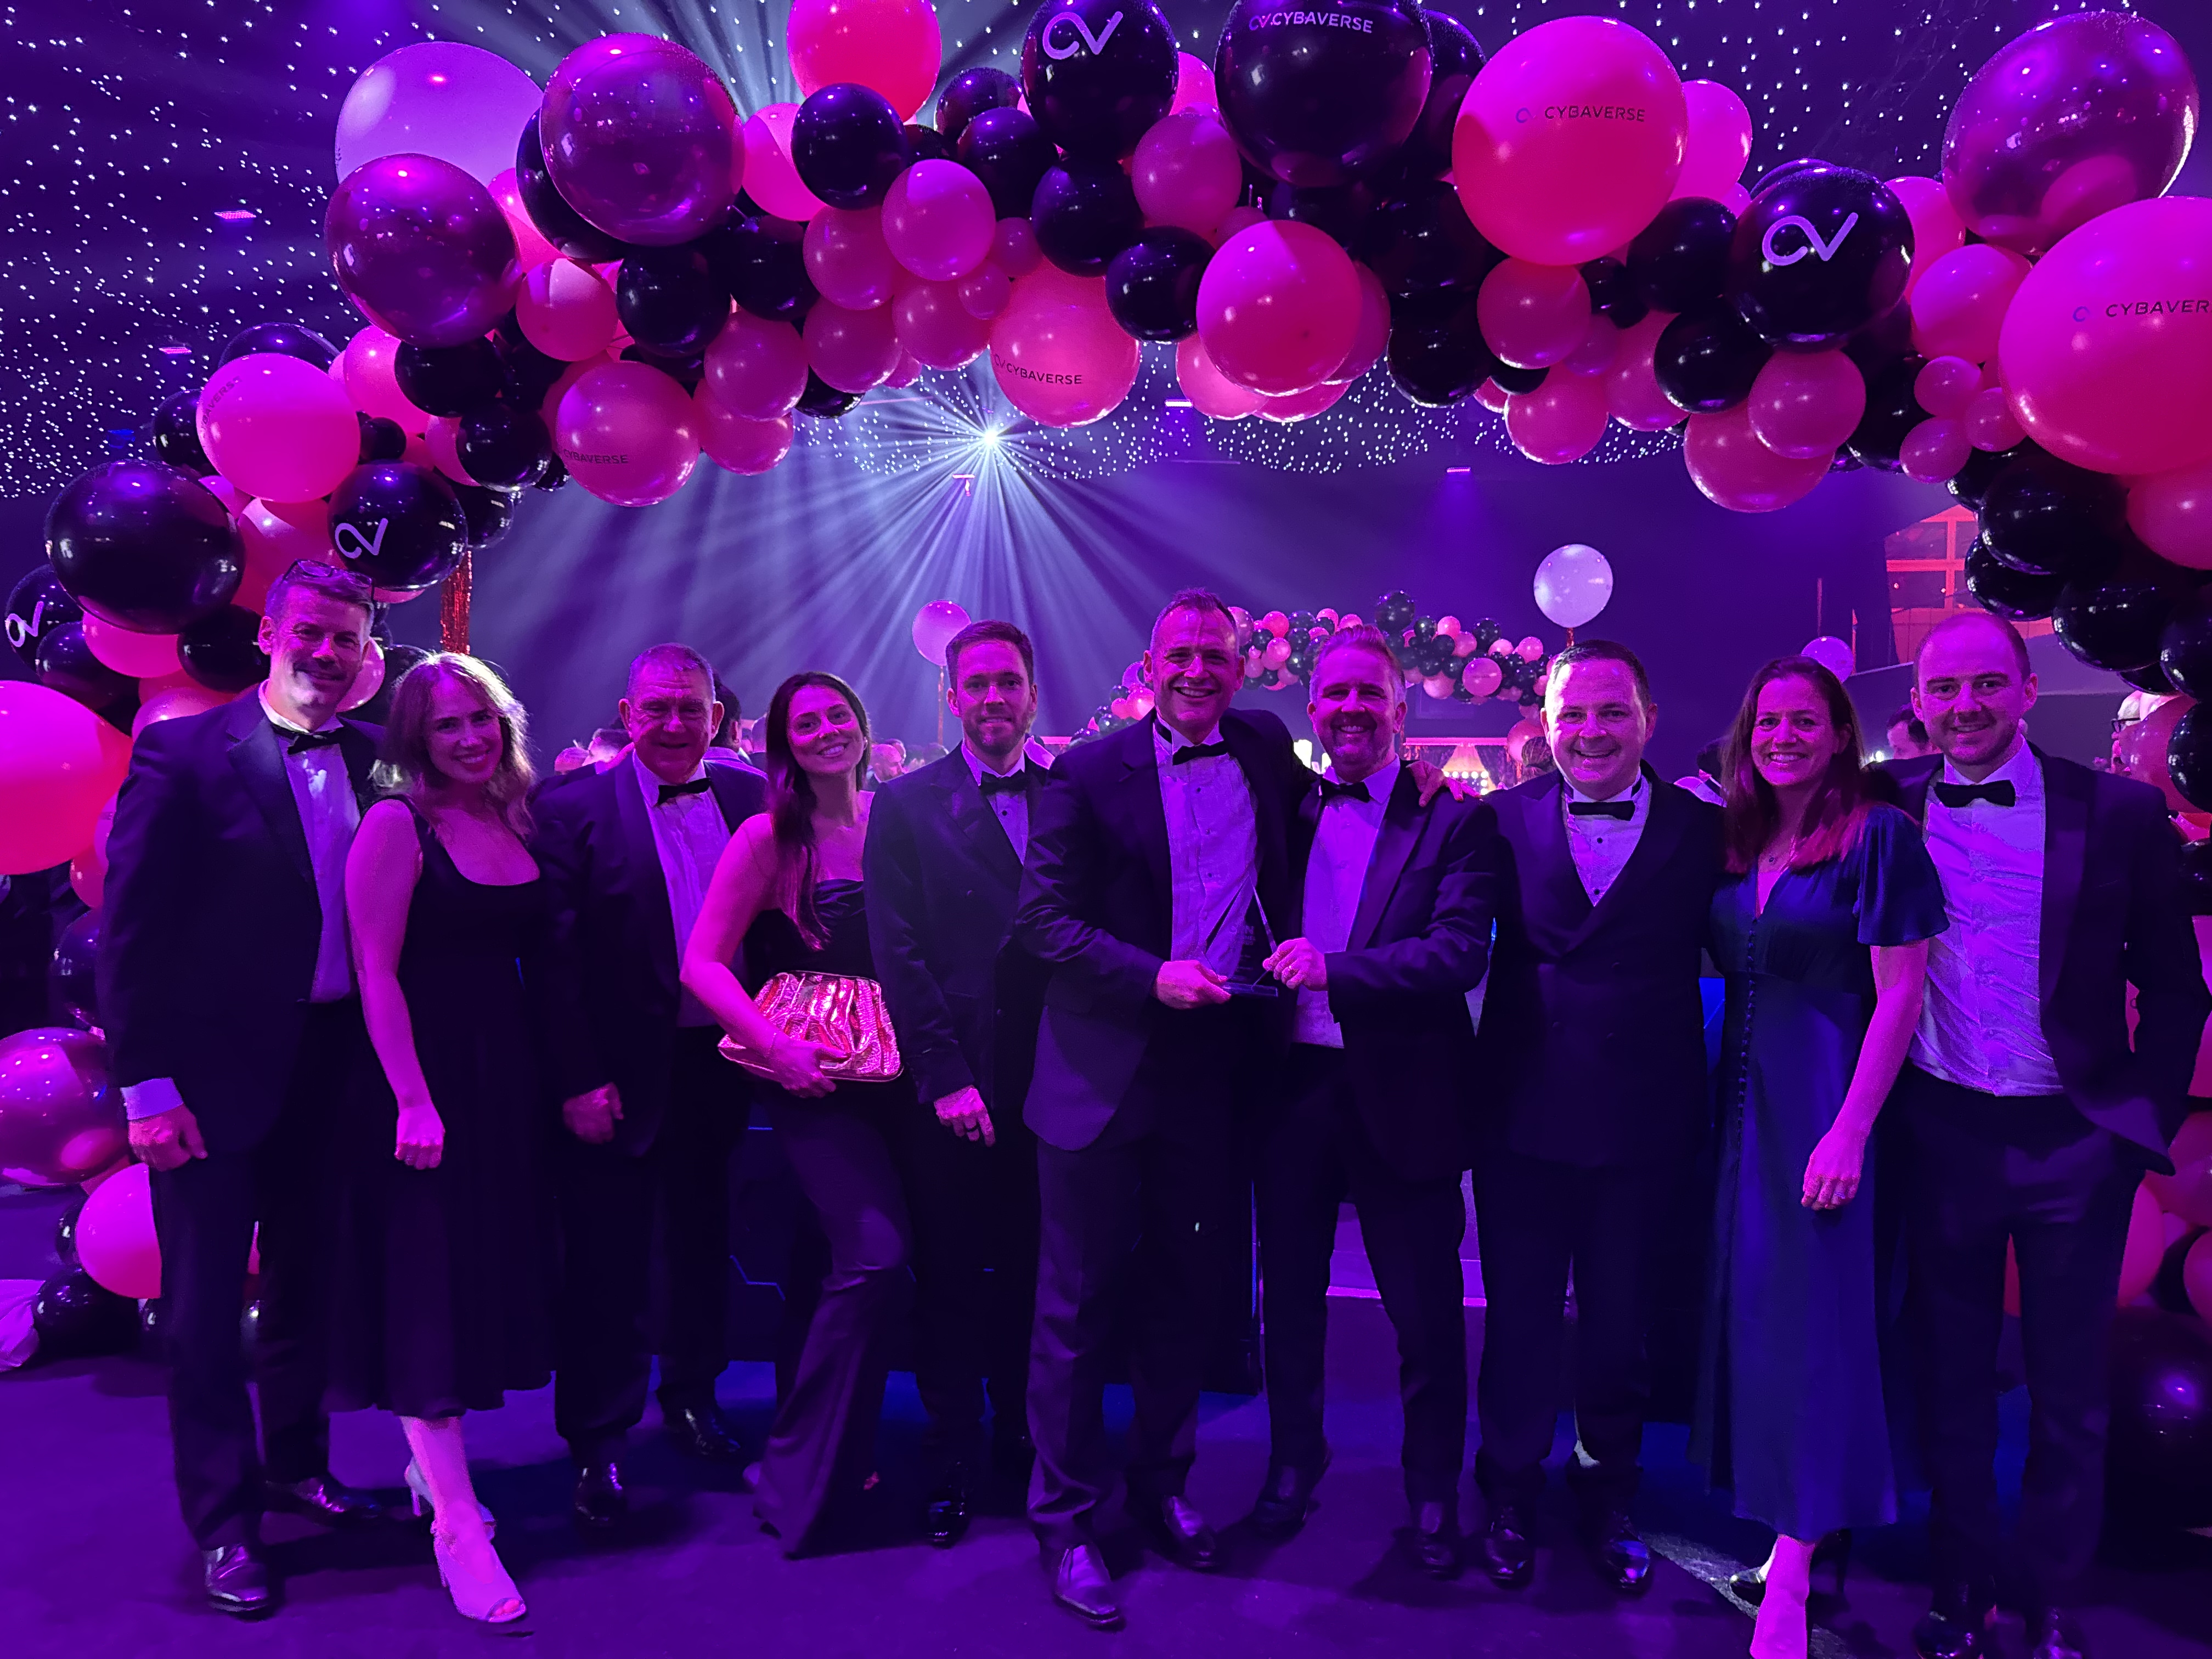
Last week, Arc were finalists at both the UK IT Industry Awards and the CRN Channel Awards. We were absolutely thrilled to receive the Judges Commended award for Managed Services Provider of the Year (£10m+).
For this category, we were asked to evidence our approach to service, our product offering, growth and sales data, HR policies, financial performance, operational processes, the impact of our work on customers and how we work alongside our partners. It’s a detailed and rigorous judging process that involves contributions from right across the business.
Geoff Wing, our CRO, said: “We’re delighted to have won the Judges Commended trophy for Managed Services Provider of the Year at the CRN Channel Awards: it reflects the hard work happening across every team and the collective effort that goes into delivering great service for our customers. Being named finalists was an achievement in itself, but bringing home a trophy is even better: thank you to the event organisers for two great evenings and congratulations to our team, our partners and our customers.”
Think you’ve got what it takes to join an award-winning team? See our open vacancies here.

Last month at the UHUK conference, our customer, East Berkshire Primary Care (EBPC), shared how a strategic technology refresh delivered resilience and flexibility...

We’re pleased to share that Arc has officially announced the appointment of Mark Darrah as our new Chief Technology Officer, marking an exciting new chapter for the...

When Jaguar Land Rover (JLR) was forced to halt production after a major cyberattack, the disruption exposed a costly truth: the company had yet to finalise its cyber...
If your organisation uses Microsoft 365, you’re already working with a powerful productivity platform. But with data flowing across Outlook, Teams, SharePoint and...